A featured contribution from Leadership Perspectives: a curated forum reserved for leaders nominated by our subscribers and vetted by the Construction Tech Review Advisory Board.
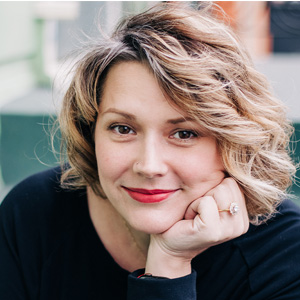
Amanda Fennell Chief Security Officer and Chief Information Officer
According to IDC, the cloud has emerged as a core foundation of renewed tech focus in APAC, leading to the region’s public cloud services spending growth of over 38% in 2020.Additionally, APAC organisations are expected to spend even more on collaboration, productivity and security tools to support remote working and innovation.
At Relativity, we’ve seen major growth in our extensible cloud platform RelativityOne with adoption increasing significantly across the globe. RelativityOne allows users to manage large volumes of data and reduce risk with proactive threat prevention, automated security processes and leading compliance certifications. Its adoption is currently growing fastest in APAC where customers and instances have more than doubled year-over-year. RelativityOne has rigorous security processes to provide 24/7 cloud security to protect clients' data while it is being worked on, which is becoming increasingly important due to the rise of cyberattacks and data breaches.
From our research in the market, security has always been a key purchasing criterion for e-discovery and compliance software. What’s interesting though is between the last few years there was a marked shift from security being the reason organisations didn’t want to move their operations to the cloud to today where security is a key reason to move to the cloud. What’s driving this shift in perspective? An increasingly evolving threat and compliance landscape.
Digital Transformation and Remote Work Drives Increased Focus on Security
The percentage of workers permanently working from home is expected to double in 2021, and by 2025, an estimated 70% of the workforce will work remotely at least five days per month. The shift to a more remote workforce and increase in collaborative work platforms comes on the heels of rapid digital transformation, making data requirements far more complex and driving a need for added scalability and security.
Before the pandemic, most organisations designed their security strategy around the assumption that remote working was the exception. As organisations shifted to a remote-work mindset, so did threat actors, taking advantage of the unanticipated change to leverage new tactics and exploit new vulnerabilities.
The changing security threat landscape for APAC has made risk mitigation and data protection strategies more crucial than ever, with 80% of APAC organisations suffering a cyber attack in 2020. Research on the threat landscape in APAC, conducted by Relativity's security team, Calder7, identifies APAC as the new "hot" target for cybercrime.
Of note, our research shows that attackers continually adapt to changing political and social events to maximise profits from cybercrime. With a majority remote workforce, the lines between personal and professional are blurred. The vulnerability of employees in a remote work environment can be used as a figurative ‘trojan horse’ to bring unsuspected malware into the workplace. Attackers are looking for any vulnerability with home workers, through VPN vulnerabilities, social engineering, poisoned ads, insertion of malicious code in repositories, online gaming and even food services. Social engineer awareness training, endpoint monitoring and response software is essential in combatting these threats.
As more workers begin to return to the office, don’t expect cybercrime to decline – it will just continue to evolve. The transition back to offices could lead to additional attacks to exploit a migrating workplace by targeting employees via social engineering methods as well as attempting to hack personal devices.
The Compliance Conundrum
Businesses have never been under more scrutiny to protect their data, while navigating new data protections has never been more complex. APAC continues to be a dynamic and growing marketplace, reacting to changing data privacy regulations and adopting processes to meet new challenges including:
• Increased obligations for corporations: Due to privacy laws as well as expectations around anti-money laundering and Foreign Corrupt Practices Act. Global businesses expanding into Asia are obligated to comply with the Department of Justice/U.S. regulations and wherever they’re operating in the region. As corporations expand in Asia, some locations lack regulations. Because of Singapore’s strong regulations and its international arbitration centre it has emerged as a hub for business.
• Managing cloud-based collaboration data for investigations and proactive compliance monitoring: Enterprise communications will continue to shift rapidly and scale from traditional channels like email toward chat and collaboration platforms. This is why Relativity has invested in technology that can connect directly to native cloud data sources for surveillance and e-discovery workflows, evolving the data paradigm from documents to include conversations. Relativity’s AI-powered communication surveillance platform, Relativity Trace, proactively detects regulatory misconduct like insider trading, collusion and other non-compliant behaviour.
How to Keep Up with the Ever-Changing Global Threat and Compliance Landscape
As the global nature of business, remote work and other factors drive an increased need for organisations to operate around the world, Relativity is committed to ensuring clients can keep up. Relativity’s cloud-based technology provides access to 11different geographies today—recently adding locations in Singapore and South Korea—and continues to expand so customers’ data can stay contained in the appropriate regions. Demand for more global availability is increasing to meet the complex challenges brought on by investigations, arbitration, litigation and compliance monitoring today. We expect this trend to accelerate as data sovereignty and personal data protection rights enter the mainstream and compliance regulations tighten up.
The changing security threat landscape for APAC has made risk mitigation and data protection strategies more crucial than ever, with 80% of APAC organisations suffering a cyber attack in 2020. Research on the threat landscape in APAC, conducted by Relativity's security team, Calder7, identifies APAC as the new "hot" target for cybercrime.
Of note, our research shows that attackers continually adapt to changing political and social events to maximise profits from cybercrime. With a majority remote workforce, the lines between personal and professional are blurred. The vulnerability of employees in a remote work environment can be used as a figurative ‘trojan horse’ to bring unsuspected malware into the workplace. Attackers are looking for any vulnerability with home workers, through VPN vulnerabilities, social engineering, poisoned ads, insertion of malicious code in repositories, online gaming and even food services. Social engineer awareness training, endpoint monitoring and response software is essential in combatting these threats.
As more workers begin to return to the office, don’t expect cybercrime to decline – it will just continue to evolve. The transition back to offices could lead to additional attacks to exploit a migrating workplace by targeting employees via social engineering methods as well as attempting to hack personal devices.
The Compliance Conundrum
Businesses have never been under more scrutiny to protect their data, while navigating new data protections has never been more complex. APAC continues to be a dynamic and growing marketplace, reacting to changing data privacy regulations and adopting processes to meet new challenges including:
• Increased obligations for corporations: Due to privacy laws as well as expectations around anti-money laundering and Foreign Corrupt Practices Act. Global businesses expanding into Asia are obligated to comply with the Department of Justice/U.S. regulations and wherever they’re operating in the region. As corporations expand in Asia, some locations lack regulations. Because of Singapore’s strong regulations and its international arbitration centre it has emerged as a hub for business.
• Managing cloud-based collaboration data for investigations and proactive compliance monitoring: Enterprise communications will continue to shift rapidly and scale from traditional channels like email toward chat and collaboration platforms. This is why Relativity has invested in technology that can connect directly to native cloud data sources for surveillance and e-discovery workflows, evolving the data paradigm from documents to include conversations. Relativity’s AI-powered communication surveillance platform, Relativity Trace, proactively detects regulatory misconduct like insider trading, collusion and other non-compliant behaviour.
How to Keep Up with the Ever-Changing Global Threat and Compliance Landscape
As the global nature of business, remote work and other factors drive an increased need for organisations to operate around the world, Relativity is committed to ensuring clients can keep up. Relativity’s cloud-based technology provides access to 11different geographies today—recently adding locations in Singapore and South Korea—and continues to expand so customers’ data can stay contained in the appropriate regions. Demand for more global availability is increasing to meet the complex challenges brought on by investigations, arbitration, litigation and compliance monitoring today. We expect this trend to accelerate as data sovereignty and personal data protection rights enter the mainstream and compliance regulations tighten up.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
